What Security and Compliance Should a YouTube Agency Have?

What Security and Compliance Should a YouTube Agency Have?
If you are a broadcaster, a rights holder, or any business with a procurement team, security can decide the deal before the content ever does. Your agency holds your accounts, your revenue data, and your audience data, so you are right to ask what protects all of it.
Four things are worth asking about: SOC 2, ISO 27001, GDPR, and Cyber Essentials. Each covers different ground, and procurement teams verify the claims, so the answers have to be true. An agency that shrugs at this, or cannot tell one framework from another, is a non-starter for serious work.
The four to ask about
These names get thrown around together, but they are not the same thing. Here is what each one actually means.
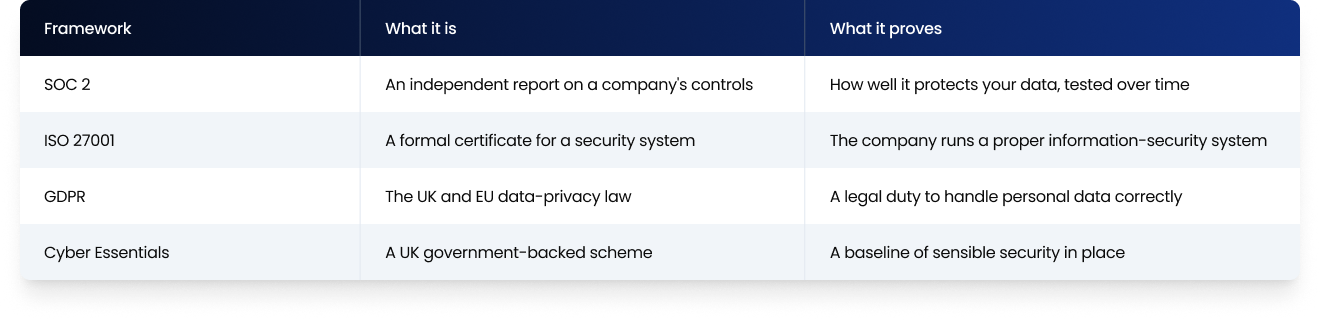
In short, ISO 27001 covers internal security processes, SOC 2 validates how a company protects customer data, and GDPR enforces legal privacy rights. There is heavy overlap between SOC 2 and ISO 27001, but they prove it in different ways: ISO 27001 results in a certificate, while SOC 2 results in an audited report. Cyber Essentials is the UK baseline that procurement teams often ask for as a minimum.
GDPR, the DPA, and the gap to mind
GDPR is the one that is not optional. Any agency handling your data in the UK or EU has to comply, and a key part of that is a data processing agreement, or DPA. A DPA is the contract that legally binds the agency to handle your data properly, setting out security duties, breach notification timelines, and who is responsible for what. Under GDPR, you should require a DPA with any vendor that processes your data.
Here is the trap to avoid. A certificate is not the same as GDPR compliance. An ISO 27001 or SOC 2 credential shows good security, but it does not automatically mean an agency meets every GDPR duty, because the law asks for things a security certificate does not cover. So treat certificates as strong evidence, not a free pass, and make sure the DPA is in place on top.
What to ask, and how to verify
Keep it simple. Ask which of these the agency holds, ask to see evidence, and ask for a DPA as standard. Two checks matter. First, make sure any certificate is current, since these are renewed yearly and an out-of-date one means little. Second, never accept "we take security seriously" with nothing behind it; certificates, written policies, and a signed DPA are the real answers.
And be wary of the opposite problem: an agency claiming a certification it does not hold. Procurement will check, and a false claim ends the conversation fast, so an honest "here is what we hold, and here is what is in progress" is worth more than a confident overstatement. At The Polar Bears we manage over two million videos for brands and broadcasters, we treat client data and account access as a serious responsibility, and we are happy to walk procurement through our security posture, our GDPR position, and the DPA. Our reporting runs on a platform Powered by Vixxi that consolidates your YouTube, Google Ads, and Google Ad Manager data in one place. For the broadcasters and publishers we work with, getting this right is often what clears the path to a contract.
FAQ
What security should a YouTube agency have?
At a minimum, GDPR compliance with a data processing agreement available as standard, plus clear answers on how it protects your accounts and data. For broadcaster and enterprise work, expect recognised frameworks too, such as ISO 27001, SOC 2, or Cyber Essentials, with evidence you can verify rather than vague assurances.
What is the difference between SOC 2, ISO 27001 and GDPR?
ISO 27001 is a certificate showing a company runs a proper information-security system. SOC 2 is an independent report on how well it protects customer data, tested over a period. GDPR is the UK and EU privacy law that legally requires correct handling of personal data. The first two are about security practice; GDPR is a legal duty.
What is Cyber Essentials?
Cyber Essentials is a UK government-backed scheme that certifies an organisation has a baseline of sensible security controls in place. It is often the minimum standard procurement teams ask suppliers to hold, and it sits below the more detailed ISO 27001 and SOC 2 in depth, but it is a useful, recognised baseline.
Does my agency need a data processing agreement?
Yes, if it handles personal data on your behalf in the UK or EU. A data processing agreement, or DPA, is the contract that legally binds the agency to handle your data properly, covering security duties and breach notification. Under GDPR you should require one with any vendor that processes your data.
Is ISO 27001 the same as GDPR compliance?
No. ISO 27001 shows strong security practice, but it does not automatically mean an agency meets every GDPR duty, because the law covers things a security certificate does not. Treat a certificate as strong evidence of good security, then make sure GDPR compliance and a signed DPA are in place on top of it.
Want an agency that clears your security checks without the hand-waving?
If you liked that why not take a look
Should Your YouTube Agency Work With Your Competitors?
Your agency might run your rival's channel too. Why agency conflict of interest matters, how good agencies keep competing clients apart, and what to ask.
What Should a YouTube Agency Put in Writing?
Most YouTube agencies dodge written commitments. What a good agency should promise: response times, reporting cadence, and fixing underperforming videos.
What Data Can You Take When You Leave a YouTube Agency?
Can you take your analytics, dashboards and custom reports when you leave a YouTube agency? What data is yours, what is not, and how to avoid lock-in.
Who Owns Your YouTube Channel When You Use an Agency?
You should own your YouTube channel, not your agency. How channel ownership works, owner vs manager access, and how to keep control on exit.
YouTube Image Posts: The New Format Most Brands Are Ignoring
YouTube image posts are moving into the main feed in 2026. What they are, why they keep your channel visible between uploads, and how brands should use them.
YouTube AI Dubbing for Multi-Market Distribution: One Video, Every Market
YouTube auto-dubbing turns one upload into 27 languages. How AI dubbing and multi-language audio tracks work, and how brands should use them in 2026.

Ready to maximise your YouTube revenue?
Get in touch and let’s begin exploring your channel’s hidden potential.